
Permission System

In Holistics, you can enforce permission control at several levels.

Data Source-Level Permission​

Administrators can share data sources to specific analysts from the Manage Data Sources page.

Data Analysts cannot view or modify database credentials information of any data source.

Behind the scene, the database user that they use to is the one specified in the data source itself. Therefore, the analyst can only run queries against the schemas and tables allowed for that database user.

Dashboard-Level Permission​

With User Access, you can share reports/dashboards/folders with specific users or groups.

Here we're going to share the Ecommerce Dashboard with a particular user or a user group. Just click on Share > Share by Users/Groups:
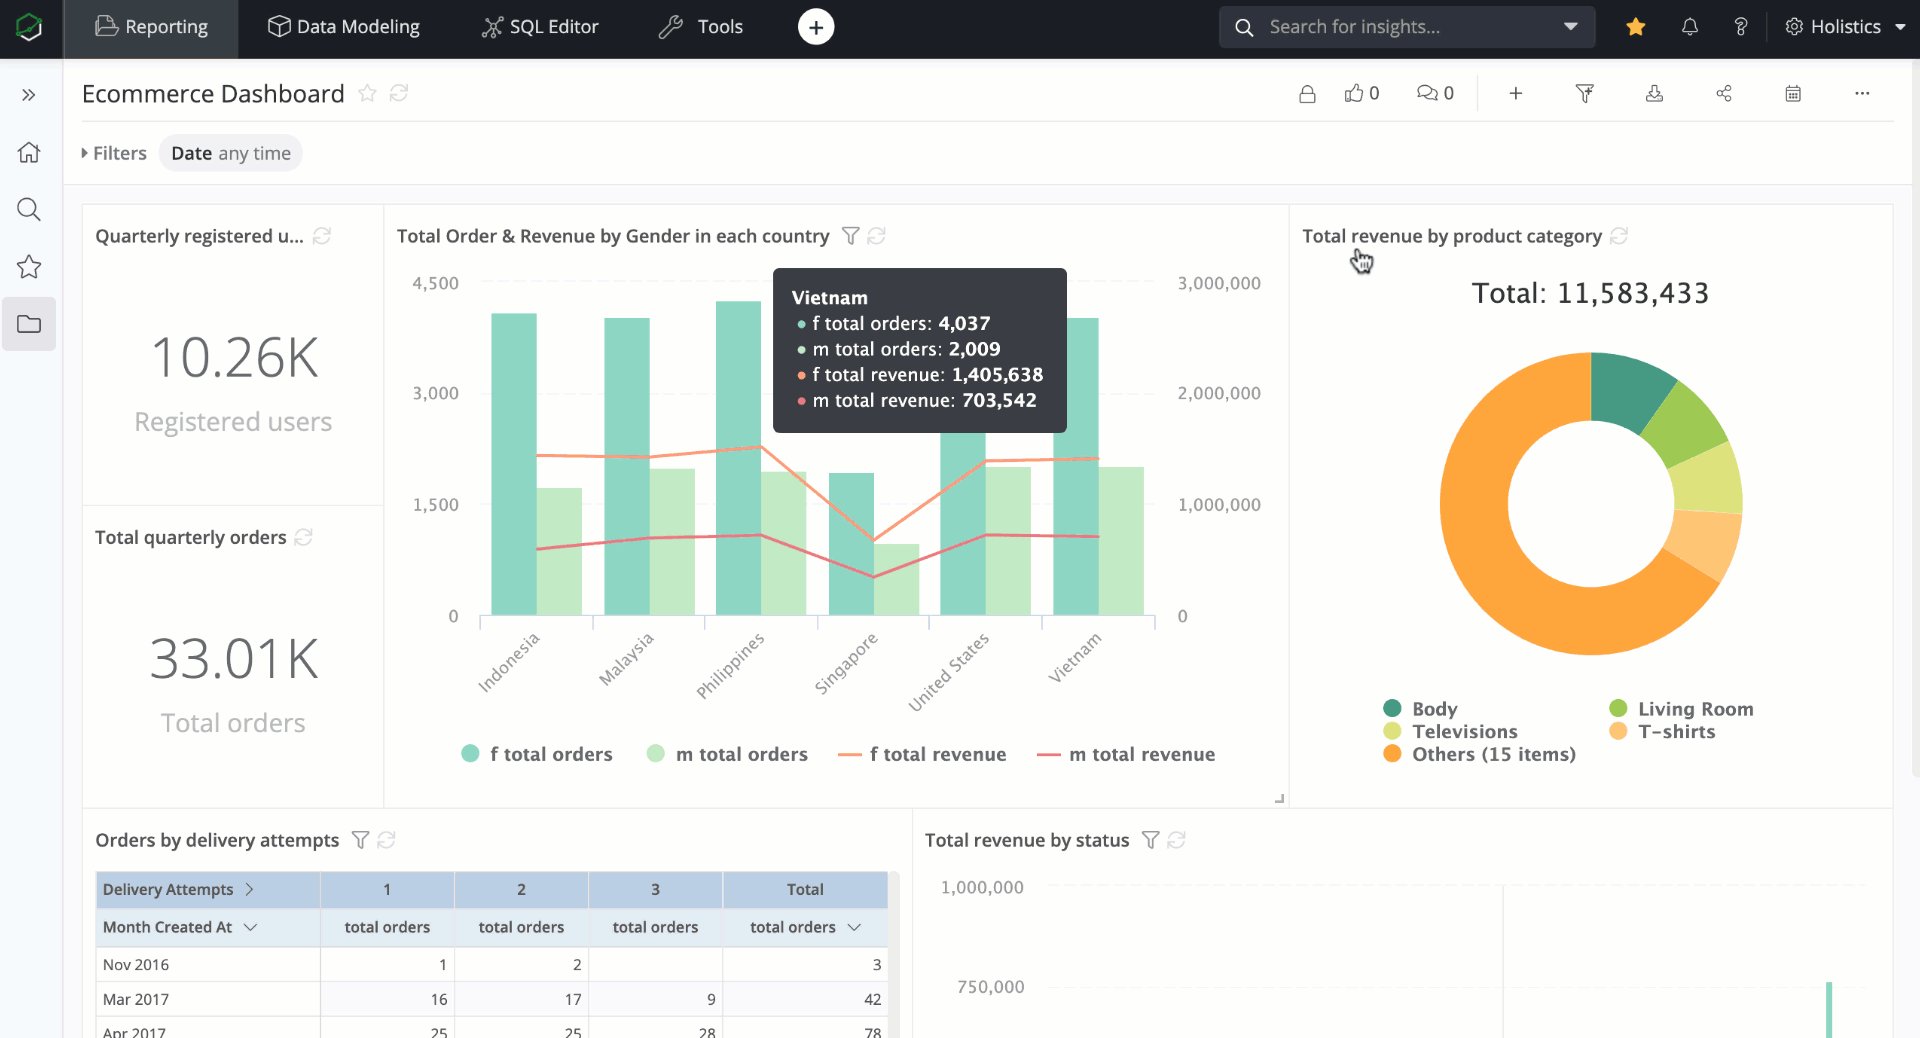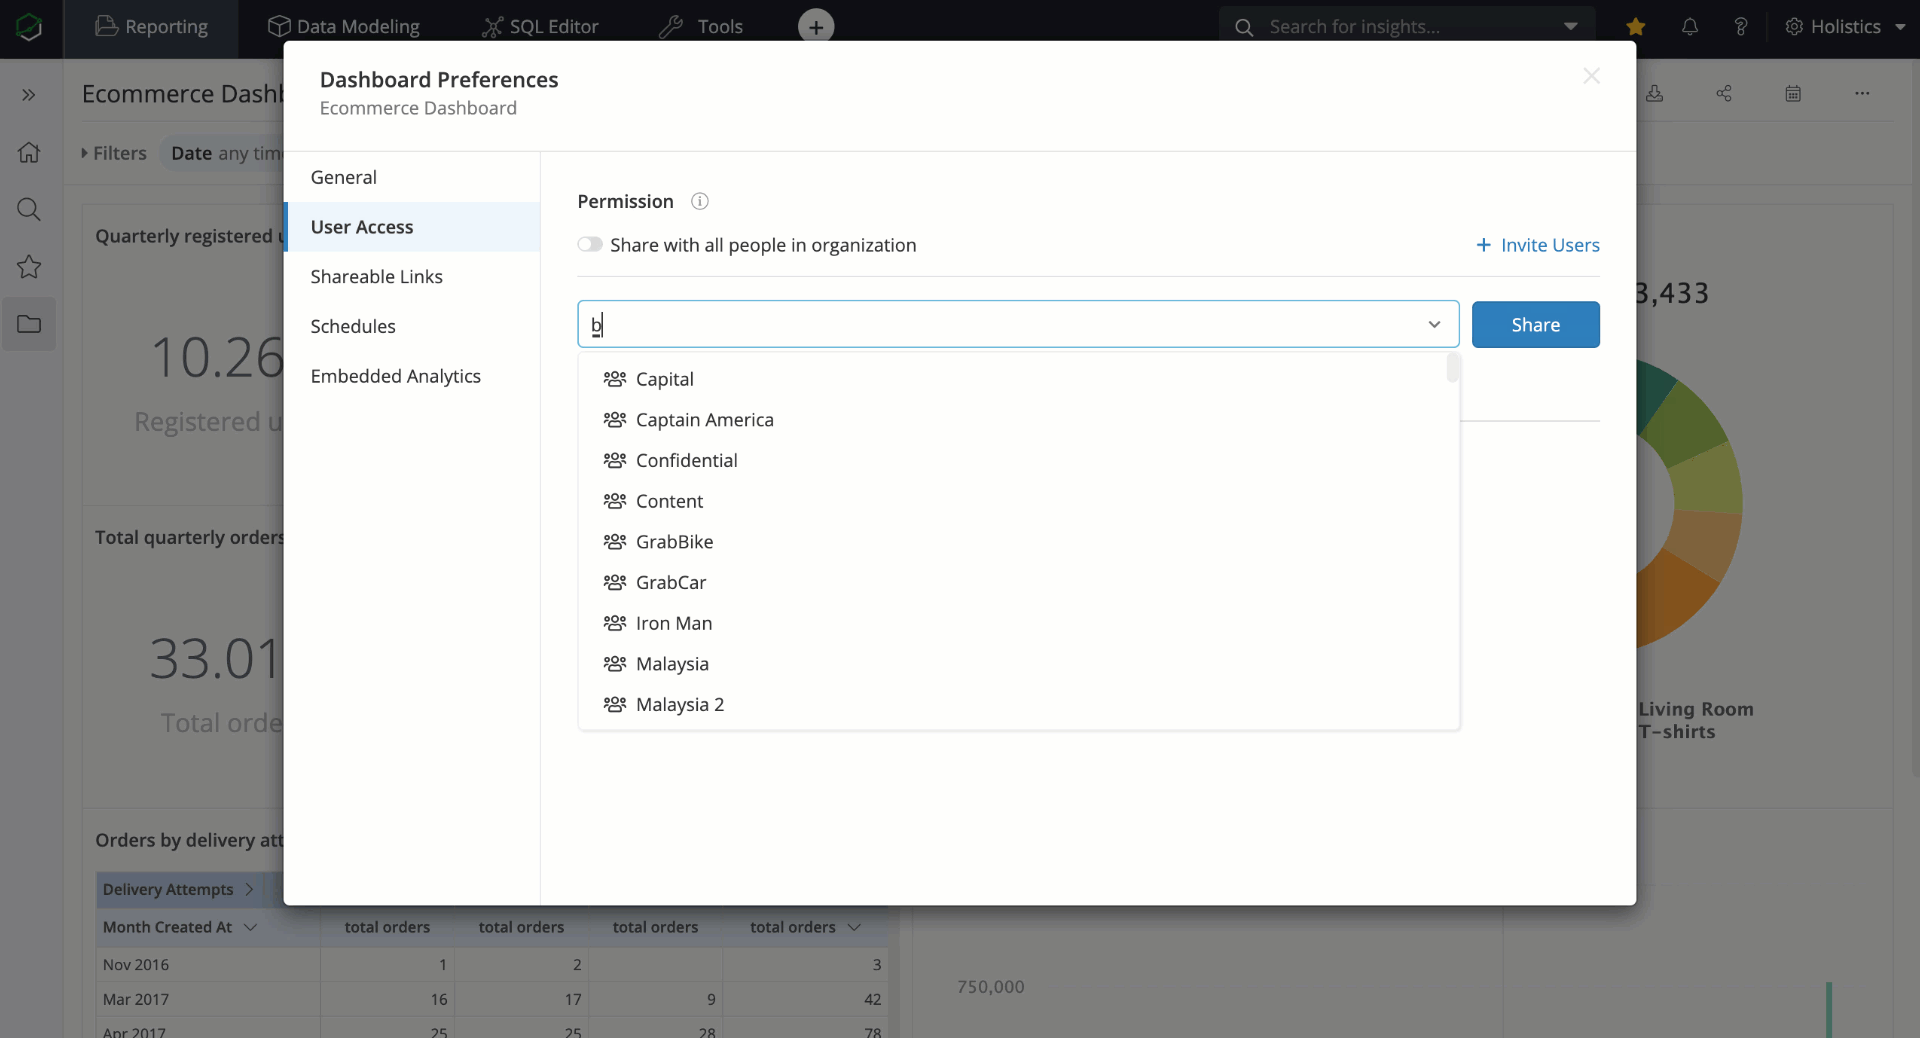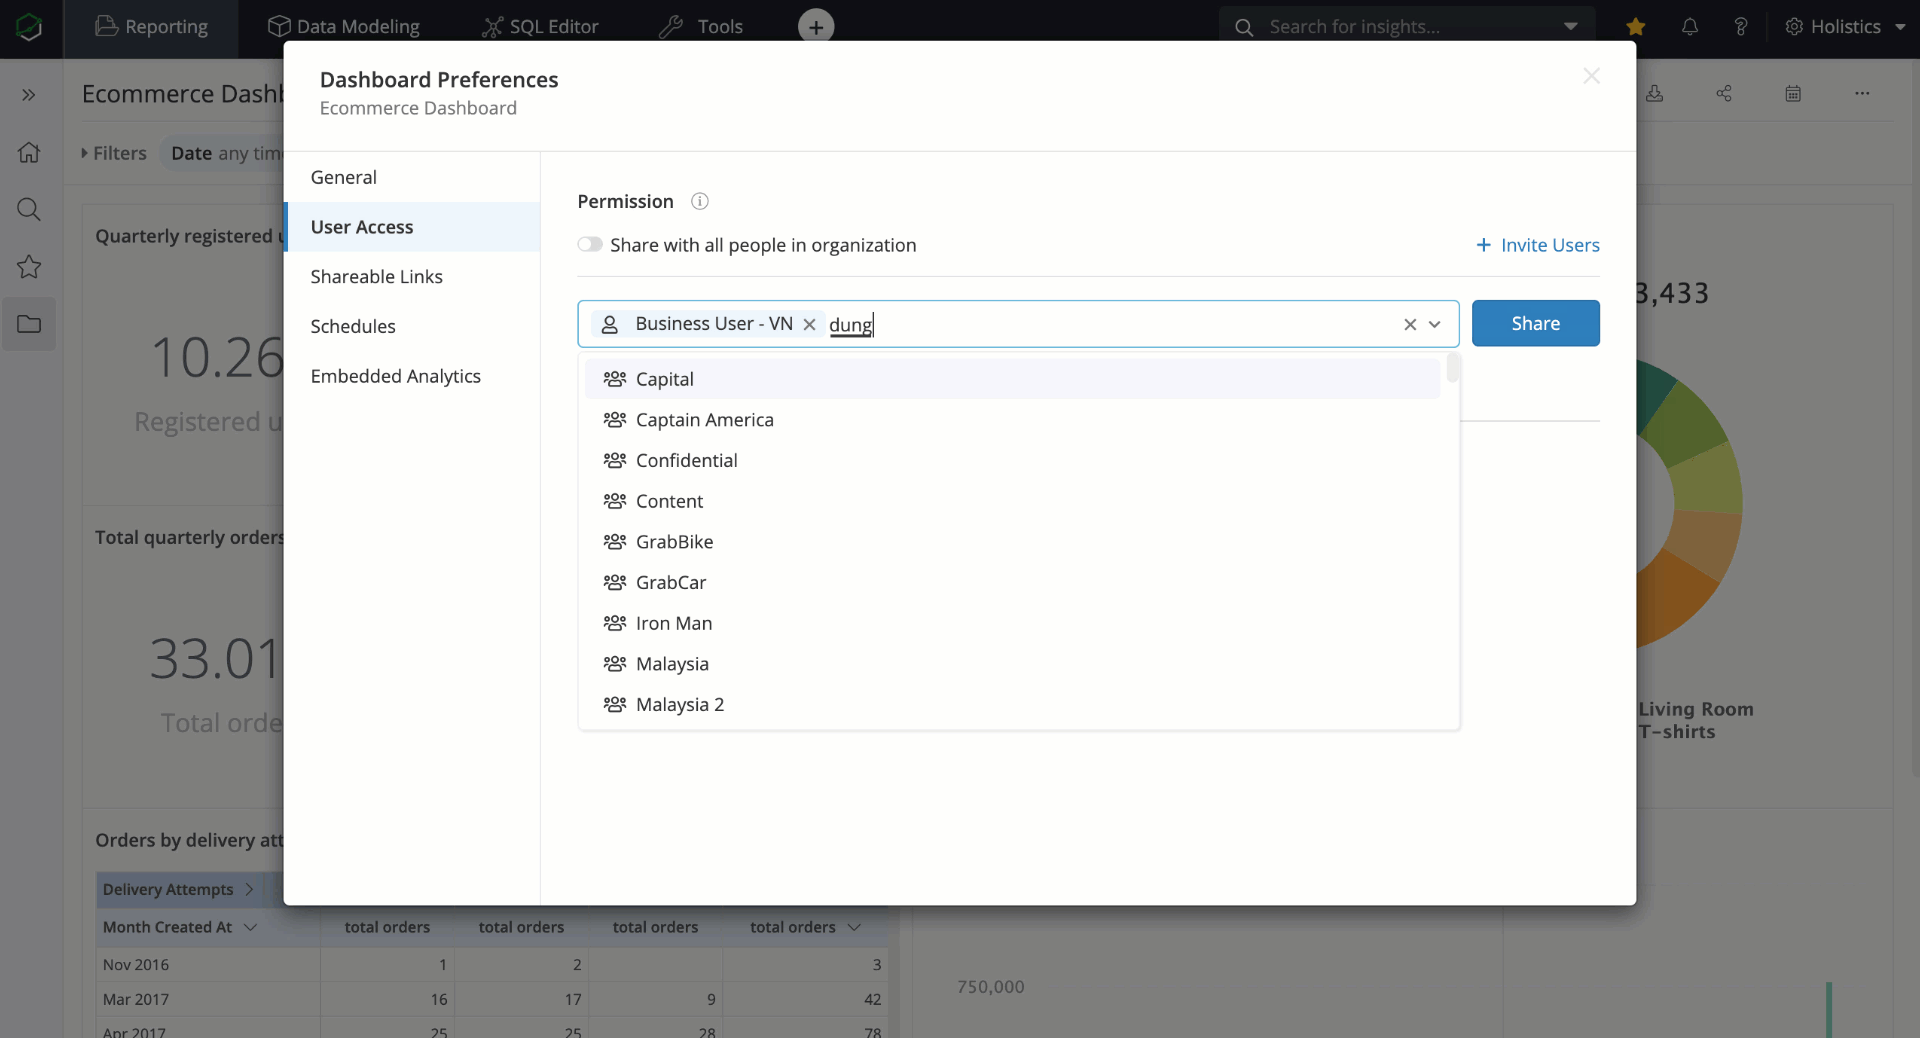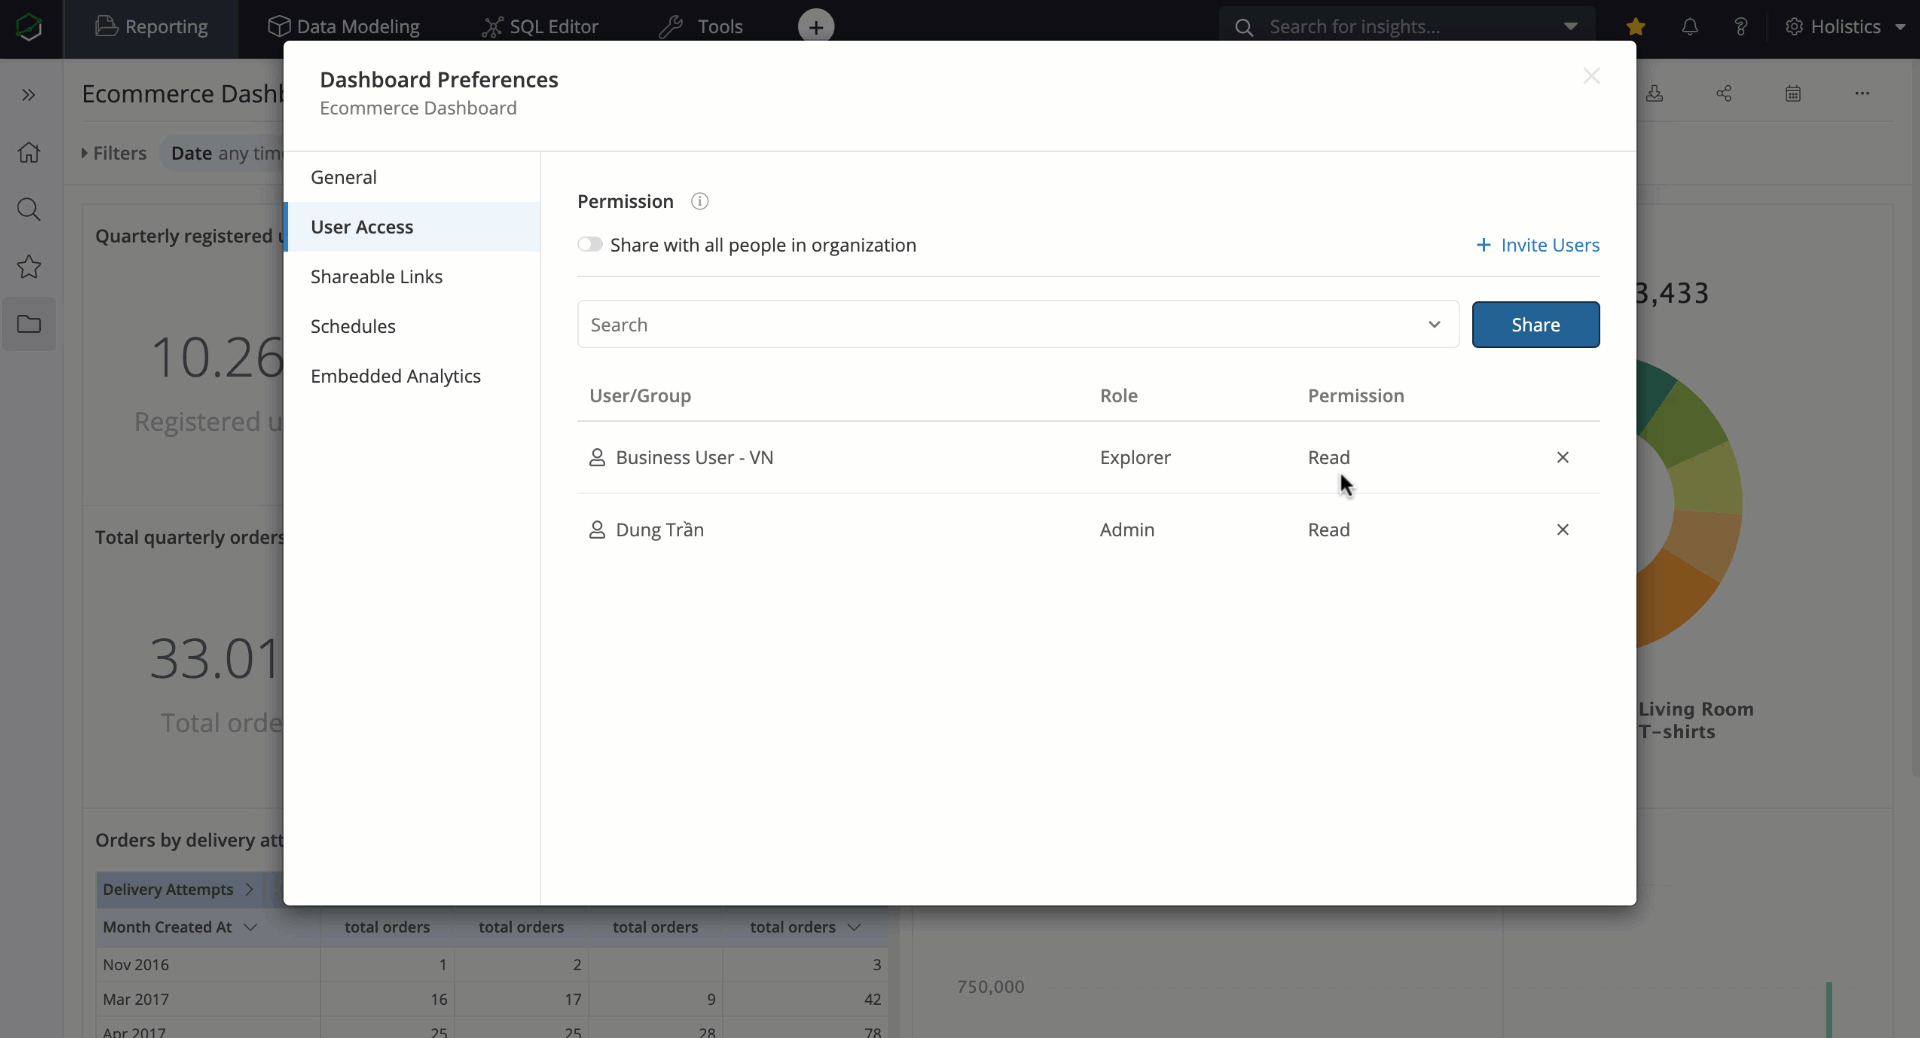
In contrast, if you want to publish my dashboard to all users, you can add All users tag as follows:

Publish my dashboard to all users

Roles and Resource Permissions Matrix​

All permissions of each role are listed below to help you decide which role to assign.

CRUD: Create, Read, Update and Delete

Holistics Permission Matrix : v3.0

DescriptionViewerExplorerAnalystAdmin
Data source
CRUD and manage data sources (access, connection credentials, etc.)❌❌❌✅
SQL Editor
Access SQL Editor and Write Adhoc Queries❌❌✅✅
Execute adhoc queries in SQL Editor❌❌✅ if data source is shared✅
Data Model
CRUD Data Model❌❌✅ on shared Data Sources only✅
Dataset
  • View Dataset in team workspace
  • Explore Dataset, and Widgets generated from this dataset
  • Create Widgets and Filters from this dataset
  • CRUD Business Calculations
  • ❌✅ if dataset is shared✅ if its data source is shared, or dataset is shared✅
    CRUD and manage datasets (including managing data models, relationships, user access and row-level permission rules)❌❌✅ if its data source is shared✅
    View custom field's definition and generated SQL❌❌✅ if its data source is shared, or dataset is shared✅
    Folder
    View any folder and its child resources (folders, dashboards)✅ if the folder is shared✅ if the folder is shared✅ but can't see the widget data if its data source is not shared with them✅
    CRUD folder and its child folders/reports/dashboards❌❌✅✅
    Dashboard
    Create dashboard ❌ ✅ in private workspace only ✅ ✅
  • View any dashboard in team workspace
  • Interact with Dashboard (Filter, Cross-filter, Drill, be drilled to)
  • Export
  • ✅ if the dashboard is shared✅ if the dashboard is shared✅ but they can only see the widget data if its data source or dataset is shared with them ✅
    Edit dashboard's meta data (title, description)❌✅ if user is dashboard owner✅✅
    Lock dashboard❌❌✅ if user is dashboard owner✅
    CRUD filters❌✅ if user is dashboard owner✅ if its datasource / dataset is shared✅
    CRUD widgets❌✅ if user is dashboard owner✅ if its datasource / dataset is shared✅
    Copy & Move dashboard/widget❌✅ in private workspace only✅ between private and team workspace✅ between private and team workspace
    Explore a widget❌✅ If its dataset is shared✅ If its data source / dataset is shared✅
    Share access with other users❌✅ if user is dashboard owner✅✅
    CRUD Data Schedules and Shareable Links❌❌✅✅
    CRUD Data Alerts❌❌✅✅
    CRUD Embedded Analytics❌❌❌✅
    Edit Cache Settings❌✅ if user is dashboard owner✅✅
    Enable / disable Drill-through / Cross-filtering❌✅ if user is dashboard owner✅✅
    Admin Management
    Workspace settings, Billing, etc.❌❌❌✅
    Invite and manage Users, User Attributes❌❌❌✅
    Log in as another user (Impersonation)❌❌✅ See usage notes for more details.✅ See usage notes for more details.
    Holistics As-code (4.0)
    Access Data Modeling layer❌❌✅ All Analysts✅

    Row-level Permission​

    Row-level Permission allows you to grant filtered access for your users (aka record-level permission), please refer to Row-level Permission to learn more.

    CRUD operations include: create, read, update and delete

    Let us know what you think about this document :)